Tao Chen @TechWithTao
Passionate AI & Cloud Evangelist - Creating Meaningful & Disruptive Platforms | Ex Microsoft - Google - Oracle | Change The World With Me - [email protected] Colorado Springs Joined August 2026-
Tweets238
-
Followers14
-
Following372
-
Likes607

A new method for skipping the mandatory Microsoft Account login in Windows 11 Home Edition has been discovered... just simply click on the small Learn more hyperlink on the Microsoft Account login page.
Oops.
The contractor that renovated the Lincoln Memorial Reflecting Pool has told the Trump administration that errors in its own work and flaws in the repair plan, not vandalism, caused the pool’s new blue liner to peel and break loose, documents show. nyti.ms/4xSMsu7

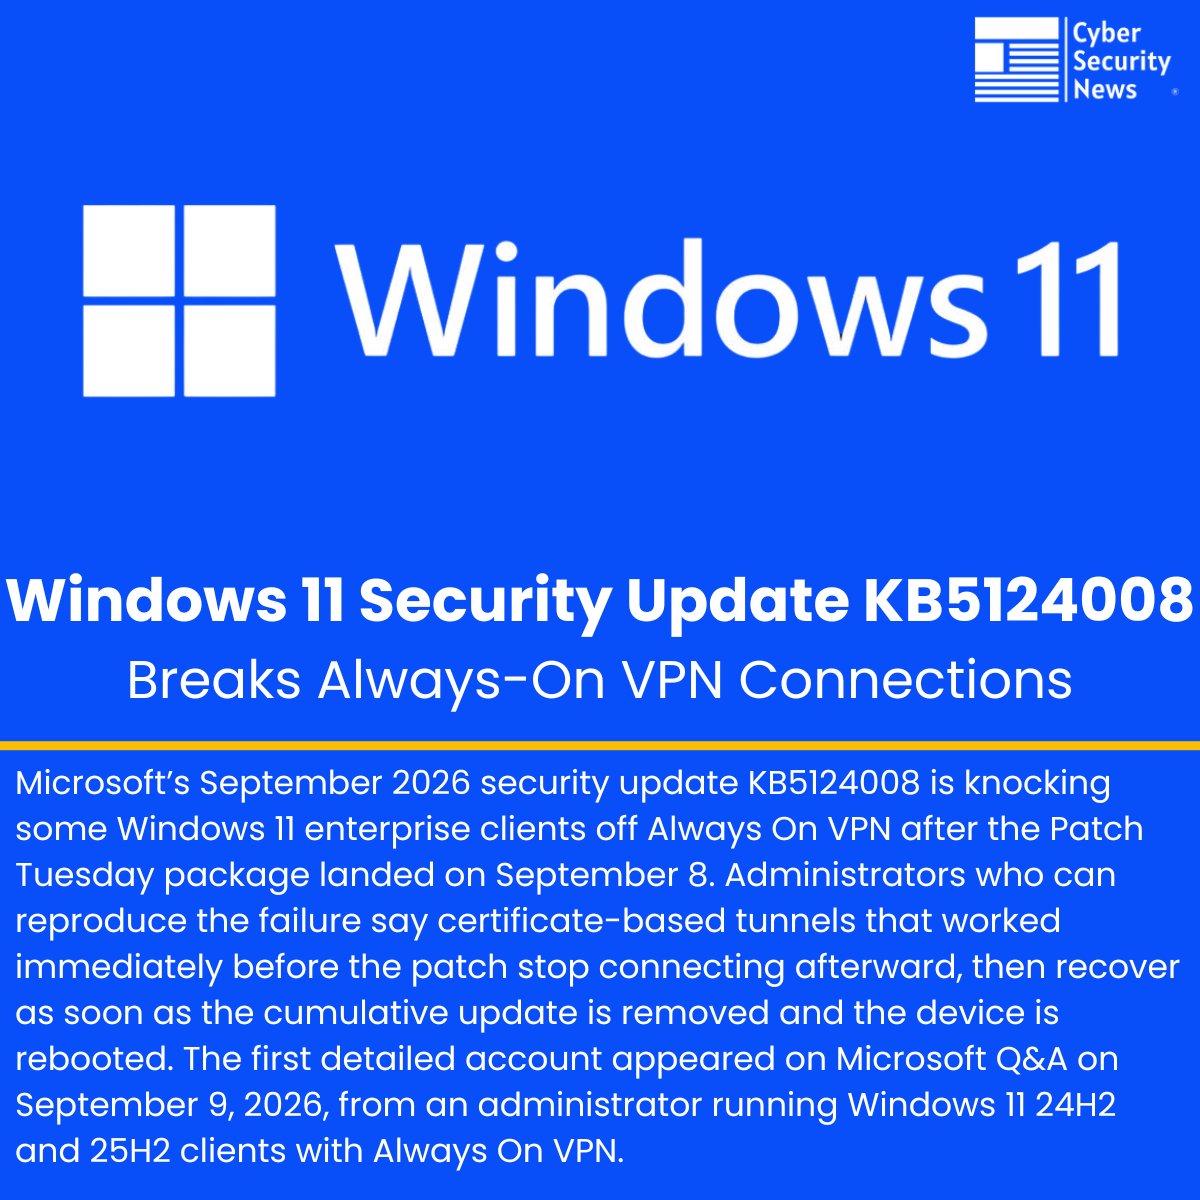
Windows 11 Security Update KB5124008 Breaks Always On VPN Connections Details: cybersecuritynews.com/windows-11-sec… Microsoft’s September 2026 security update KB5124008 is knocking some Windows 11 enterprise clients off Always On VPN after the Patch Tuesday package landed on September 8. Administrators who can reproduce the failure say certificate-based tunnels that worked immediately before the patch stop connecting afterward, then recover as soon as the cumulative update is removed and the device is rebooted. The first detailed account appeared on Microsoft Q&A on September 9, 2026, from an administrator running Windows 11 24H2 and 25H2 clients with Always On VPN. #cybersecuritynews
A good watch!
This is the interview Trump’s FCC doesn’t want you to see. We’re not just going up against the most corrupt politician in Texas. We’re going up against this entire corrupt system.
September Windows Server updates break Remote Desktop Services bleepingcomputer.com/news/microsoft… bleepingcomputer.com/news/microsoft…
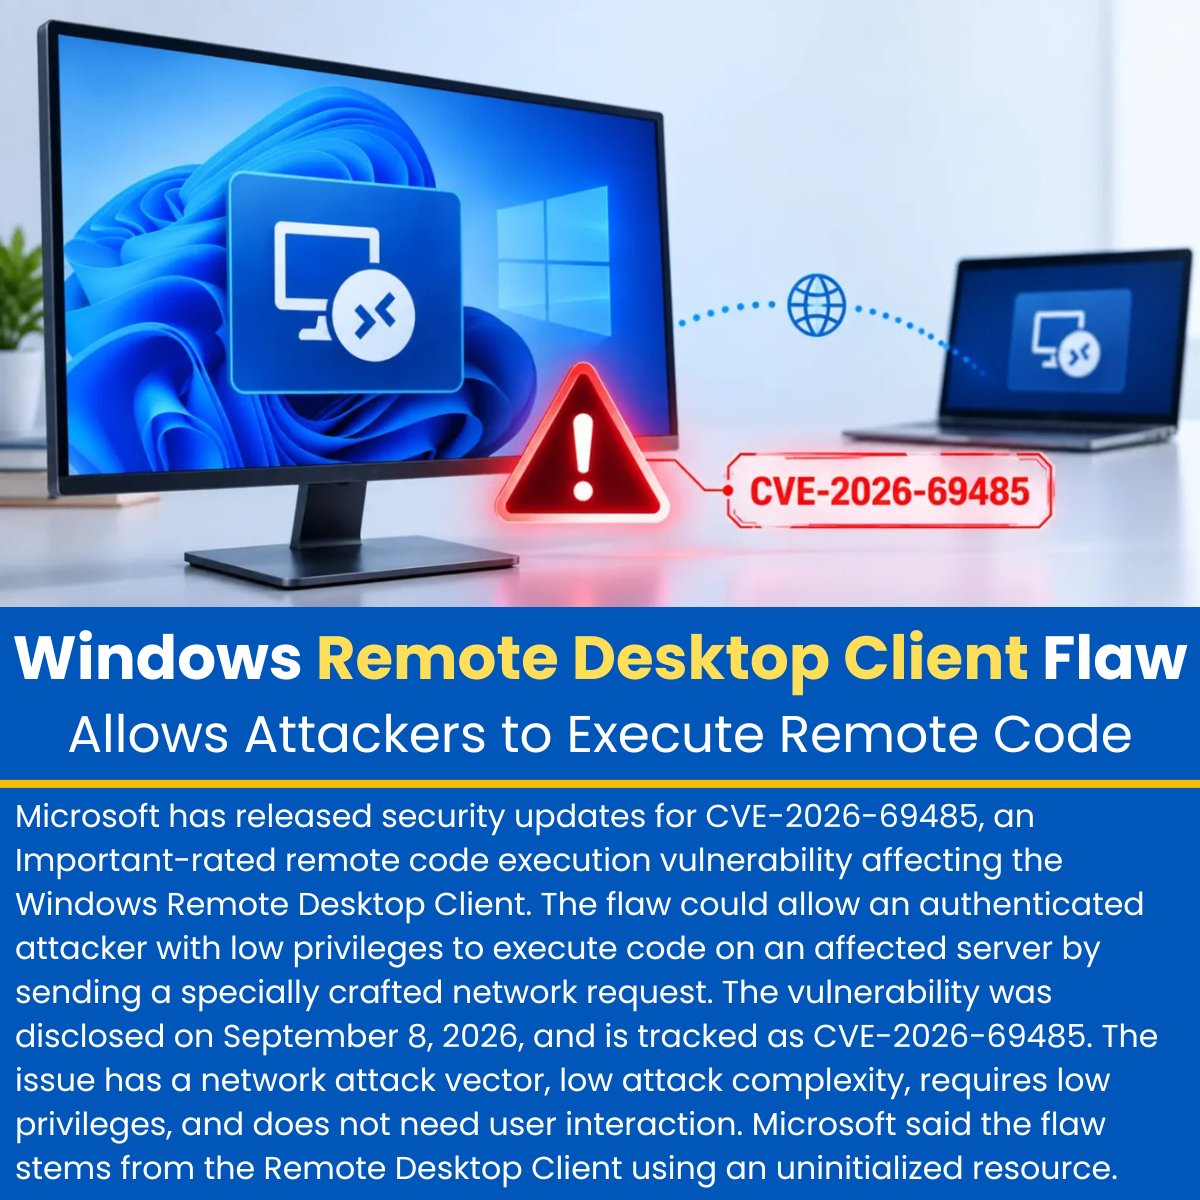
⚠️ Windows Remote Desktop Client Vulnerability Allows Attackers to Execute Remote Code Details: cybersecuritynews.com/windows-remote… Microsoft has released security updates for CVE-2026-69485, an Important-rated remote code execution vulnerability affecting the Windows Remote Desktop Client. The flaw could allow an authenticated attacker with low privileges to execute code on an affected server by sending a specially crafted network request. Microsoft disclosed the vulnerability on September 8, 2026, and tracks it as CVE-2026-69485. The issue has a network attack vector, low attack complexity, requires low privileges, and requires no user interaction. Microsoft said the flaw stems from the Remote Desktop Client using an uninitialized resource. #cybersecuritynews

Microsoft has dropped CVE-2026-69730: a Windows DNS Server RCE with a 9.8 CVSS score. No authentication. No user interaction. Low complexity. No mitigation. No workaround. Basically, it doesn’t knock on the door; it lets itself in, makes a brew and starts executing code. Patch it. 😂
Cisco confirms CVE-2026-20079 Secure FMC flaw exploited in attacks bleepingcomputer.com/news/security/… bleepingcomputer.com/news/security/…
🤣🤣
If Democrats flip the House and Senate everyone will get a $10,000 dividend, and a pony, and free ice cream for life. (Folks can also choose free yogurt for life, because we’re Democrats after all).
Here we go again! 🍿

RAPID RESPONSE UPDATE: Huntress has produced a proof of concept (PoC) of a new vulnerability chain (CVE-2026-86206 & CVE-2026-86207) in N-central. This is distinct from the August flaws, allowing attackers to bypass access controls to create unauthorized administrative accounts.

Every time you plug a USB device into a Windows machine the operating system writes a record to the registry. That record persists indefinitely after the device is removed, after the device is destroyed, and after you have forgotten the device ever existed. The registry keys that store this information are located at HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Enum\USBSTOR and HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Enum\USB. Every device that has ever connected gets an entry containing the device type, manufacturer, product name, hardware ID, and a unique serial number specific to that device. A separate key at HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\DeviceClasses stores the timestamps of first connection, last connection, and last removal for every device. Windows also writes the drive letter assigned to the device and the volume name into additional registry locations. The Windows Event Log adds another layer. Event IDs 2003, 2004, and 2100 in the Microsoft-Windows-DriverFrameworks-UserMode log record connection and disconnection events with timestamps precise to the millisecond. The practical implications go in two directions. From a forensics perspective this is invaluable. Digital investigators can reconstruct exactly which USB devices were connected to a machine, when they were connected, how long they were connected, and what drive letter they were assigned. That evidence has been used in criminal prosecutions, corporate investigations, and data theft cases. The registry does not lie and it does not forget. From a privacy perspective every USB device you have ever connected to a Windows machine has left a permanent trace that survives removal of the device itself. A flash drive containing sensitive data that you destroyed still has its serial number recorded in the registry of every machine it ever touched. The only way to remove these records is manually deleting the relevant registry keys or using dedicated tools like USBDeview or DriveCleanup. Windows does not offer a native cleanup mechanism for this data. Your machine remembers every device. You do not have to.
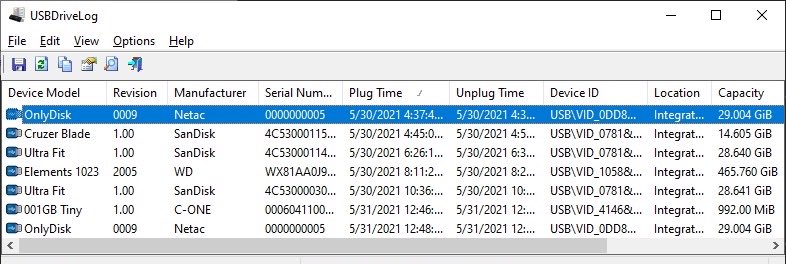
Windows keeps a permanent record of every USB device you’ve ever plugged in even after it’s removed.
@krassenstein She’s trying hard to get that press secretary role. 🤣
Another day, another 0-day!
🚨 Critical Chrome 0-Day Vulnerability Actively Exploited in the Wild | Source: cybersecuritynews.com/chrome-0-day-f… Google has released an emergency Chrome security update that fixes a critical zero-day vulnerability already being exploited in real-world attacks. The flaw, tracked as

@Broncos @Broncosthunder @artatequila Let’s go broncos!!! 🏈


Emma Dove 🕊️ @Gentle91Mind
500 Followers 878 Following emotionally attached to aesthetics 🎨 follow back

Jessica Allen @Jessica_alllen1
311 Followers 2K Following Multi-Asset Trader 📍🇺🇸United States ▪️Trader,Mentor & Entrepreneur DM me to get started 💹📶

Mark Marko @MarkMarkohk2k
57 Followers 459 Following
Gawshoo @Gawshoo48552
10 Followers 183 Following
LIV Morgan @liv_morgan2265
3 Followers 305 Following I’m open and a conversation lady dm meat vibes Service only
cloudieash @cloudieash456
41 Followers 753 Following my camera roll is basically game clips 🎮 blurry sunsets and food pics 🍜
Tom Williams @tommyboy0690
75K Followers 71K Following Lifelong Democrat Want to spread the truth, Owner of Boston Movie Screeners Meet Up Group https://t.co/AJLd0z2S7V @https://t.co/AJLd0z2S7V No DMs, please
HarleyVale @Gerda3367425
7 Followers 287 Following Enjoying the journey one day at a time Enjoying the beauty of now.

Mark 🍁 @Markfry809
82K Followers 54K Following 🇨🇦🌊🌊🌊🇺🇸Canadian emotional supporter for sane Americans who’ve had their lives ruined by Trump. Need a shoulder to lean on and I’ll be that guy.
Dave Kennedy @HackingDave
233K Followers 6K Following Founder @Binary_Defense @TrustedSec Co-Owner https://t.co/NUvgPUifL0. @WeHackHealth Pod. God + Family/Hacker/CSO/USMC/Intel/Fitness. Make the world a better place.
The Washington Sun @washingtonsun
241K Followers 167 Following Shining a light on Washington. NOTUS is now The Washington Sun. Metro coverage: @washsunmetro Analysis, ideas and narratives: @washsunperspect

Steve Paris @SteveParis1
75 Followers 70 Following Building apps, games and random ideas using AI, probably spending way too much time testing new models. Dog person 🐕
Matt Johansen @mattjay
46K Followers 2K Following Founder of @vuln_u | Long Island elder emo surviving in ATX | AI and Cybersecurity news from an 18yr industry vet


Steve Schmidt @SteveSchmidtSES
1.4M Followers 235 Following
Alex Vindman 🇺🇸 @AVindman
956K Followers 2K Following Dad. Husband. Vet. Ex National Security Council/White House Staff. Florida Man.
Former Fetterman Staf... @FettermanStaff
163K Followers 2 Following A group of former Fetterman staffers who are disgusted with what he's become. Here to share our stories & make sure Pennsylvanians know exactly who he is.
Michael Steele @MichaelSteele
372K Followers 2K Following C0-Host @Weeknightmsnow Former RNC Chairman, Former Lt. Gov. Maryland


Nikhil @nikhilx22
1K Followers 1K Following I write about AI , Robotics and build tools. Launch your app 🚀 https://t.co/JnnodrRORJ
OpenAI @OpenAI
5.3M Followers 4 Following OpenAI’s mission is to ensure that artificial general intelligence benefits all of humanity. We’re hiring: https://t.co/dJGr6LgzPA
stanchris @stanchrisss
90K Followers 224 Following Youtuber / creator / tiktoker / guy posting stuff 📷 insta: stanchris (yes i have one👇)
Zachi @iam_zachi
4K Followers 245 Following I develop and do some security stuff 38x CVE‘s 🙋🏽♂️ https://t.co/lX5HKRFNV9 📱 https://t.co/wax7xYiQmZ 🧩 https://t.co/5g1lrZOh8A
rekdt @rekdt
17K Followers 852 Following // malware degenerate // sr cybersecurity leader, megacorp usa // @sec_defcon daemon // misery @despairware // take sincerely at your own risk
National Debt Tweets @NationalDebt
153K Followers 9K Following Based on Treasury data. (+) or (-) means up or down from previous day. Run by @pgpfoundation. Let lawmakers know you care: https://t.co/K8VqnczoiI

Brian Krassenstein @krassenstein
999K Followers 456K Following AI, Technology, Crypto, Web3, Political commentary - Follow My Brother: @EdKrassen. Linktree: https://t.co/5Sol7rx2c6
Aaron Rupar @atrupar
1.1M Followers 6K Following journalist. sign up for my newsletter, Public Notice (link below). Powered by @SnapStream (more info: https://t.co/2oHPuuFBnN).
Kimiyah-Vette C8 @boujiebaddie
3K Followers 2K Following "Using my voice for the voiceless. 📢 Human rights are non-negotiable. 🗳️"Culturally-inspired ✨#SmokeFleet. #Resist. #BlueCrew
Senator Adam Schiff @SenAdamSchiff
3.4M Followers 905 Following Husband. Father. U.S. Senator for California. Fighting for an economy that works for everyone and for our democracy.
Marc E. Elias @marceelias
839K Followers 185 Following Founder @democracydocket. Chair of Elias Law Group. My dog's name is Blue.
Mueller, She Wrote @MuellerSheWrote
722K Followers 13K Following I have the same handle everywhere. Subscribe to my FREE newsletter: https://t.co/QZeOoeMenI Secure contact: [email protected]
Laurence Tribe 🇺�... @tribelaw
1.4M Followers 784 Following “We are living through a revolt against the future. The future will prevail.” — Anand Giridharadas
Amy Klobuchar @amyklobuchar
1.9M Followers 105K Following U.S. Senator from Minnesota. Candidate for Governor.
Joyce Alene @JoyceWhiteVance
1.0M Followers 2K Following Giving Up Is Unforgivable|UALawSchool|MSNOW|#SistersInLaw & Cafe Insider|Obama US Atty |25 year fed'l prosecutor |Wife & Mom of 4 |Knits a lot |Now on Substack
Jen Psaki @jrpsaki
1.3M Followers 1K Following Mom of two, proud politics and policy nerd, Host of @PsakiBriefing on @MSNOWNews, Tues-Fri at 9pm ET
Mary L Trump @MaryLTrump
1.7M Followers 1K Following Mom. Wife. Writer. Defender of democracy. https://t.co/8exl2wxVXu
Duty To Warn 🔉 @duty2warn
430K Followers 9K Following Mental Health professionals warning about Trump. Catch our Podcast, "Shrinking Trump" on the Really American Network with Dr. John Gartner and Dr. Harry Segal
Adam Kinzinger (Slava... @AdamKinzinger
1.1M Followers 2K Following Dad. Husband. Former GOP congressman. Voted to impeach Trump. Now fighting for our democracy. Lt. Col. @AirNatlGuard (ret). Founder @thecountryfirst.
Hakeem Jeffries @RepJeffries
1.0M Followers 1K Following Brooklyn Congressman. Leader @HouseDemocrats. Work hard. Stay focused. Deliver results #ForThePeople.
Red Hat @RedHat
303K Followers 1K Following The leading provider of enterprise open source solutions, using a community-powered approach to deliver Linux, hybrid cloud, edge, and Kubernetes technologies.
GitHub @github
2.7M Followers 334 Following The AI-powered developer platform to build, scale, and deliver secure software.
Rep. Jamie Raskin @RepRaskin
945K Followers 6K Following Proudly serving Maryland's beautiful Eighth Congressional District and leading @HouseJudiciary Committee Democrats in Congress.
Oscar the Grouch @OscarTheGrouch
315K Followers 13 Following Officially grouchy from Sesame Street. Scram!
Reverend Raphael Warn... @ReverendWarnock
1.2M Followers 881 Following Pastor. Advocate. Savannah born & raised. @Morehouse alum. Senator from Georgia.

Imagination Library @dollyslibrary
207K Followers 18 Following Official: Dolly Parton's Imagination Library - International book gifting program for children from birth to age five.
The Linux Foundation @linuxfoundation
593K Followers 9K Following A nonprofit organization enabling mass innovation through open source. #linux #kubernetes #riscv #hyperledger #anuket #openssf #openjs #o3de and more!
Have I Been Pwned @haveibeenpwned
180K Followers 1 Following Check if you have an email address or password that has been compromised in a data breach. Created and maintained by @troyhunt.
Sam Altman @sama
6.2M Followers 1K Following The mission of OpenAI is to ensure that AGI benefits all of humanity

Trends for United States
You might like