John Doe @nullfalse0
Open-source intelligence Joined June 2026-
Tweets61
-
Followers5
-
Following100
-
Likes0

🚨 IDSCAN.NET OFFICIALLY CONFIRMS DATA BREACH — GOVERNMENT ID INFORMATION POTENTIALLY EXPOSED IDScan.net has officially confirmed a cybersecurity incident involving unauthorized access to information stored in its cloud environment. The identity verification company says it received information around September 1 indicating that certain data may have been accessed without authorization. IDScan subsequently launched an investigation and engaged third-party cybersecurity specialists. The company has now determined that an unauthorized third party may have accessed and/or COPIED customer information stored within customer accounts on the IDScan.net cloud. Potentially affected information includes: * Full names * Driver's license numbers * Other government-issued identification numbers IDScan says it has taken steps to secure its systems and currently has no evidence of ongoing unauthorized access. Potentially affected records are those that entered its systems BEFORE September 1, 2026. The company is reviewing the affected information to identify impacted individuals and says it will provide notifications and free credit-monitoring services where appropriate. 🚨 WHAT ABOUT THE REPORTED 153 MILLION DRIVER'S LICENSES? This is an important distinction. Earlier reporting linked IDScan.net to a massive dark-web dataset advertised through the Nexus marketplace, reportedly containing approximately 153 million driver's-license records and millions of other identity documents. IDScan's new disclosure confirms unauthorized access to its cloud environment and potential copying of government-ID information. However, IDScan has NOT confirmed that 153 million figure as the number of people or records affected. The full scope of the incident remains under investigation. ⚠️ Analyst Note: This is an unusually sensitive category of breach. Passwords can be changed. Payment cards can be replaced. Government-issued identity information is substantially more difficult to remediate once compromised. And identity-verification providers inherently represent high-value aggregation points because their platforms may process identity documents on behalf of many different organizations. For defenders, this incident raises a broader supply-chain question: How long should identity-verification providers retain the documents and identity attributes they process after verification is complete? Data that no longer needs to exist cannot later become breach inventory. Official source — IDScan.net: idscan.net/press-release/… #DDW #IDScan #DataBreach #IdentityTheft #CyberSecurity


IDScan Confirms Breach Tied to 153 Million Stolen Driver’s Licenses bit.ly/4A9U90m
AI is moving beyond chatbots. The next wave is agentic: AI agents that can take action on behalf of users through trusted delegation. But scaling that innovation across the enterprise requires more than excitement—it requires control, security and visibility. Jeetu Patel and DJ Sampath explore the shift from chatbots to agents and how Cisco Cloud Control is helping enterprises manage AI innovation with confidence. Watch their full conversation: cs.co/6010B17ZYO
China-based AI companies are illicitly distilling U.S. frontier AI capabilities. Read NSA’s new report, co-sealed with @FBI, @CISAgov, highlighting AI knowledge distillation, TTPs used, and recommended mitigations: media.defense.gov/2026/Sep/08/20…


Several major AI services experienced outages yesterday, with disruptions affecting users across multiple regions. ChatGPT, Claude, Grok, Gemini, Cursor and others all saw spikes in reports on Downdetector. ChatGPT received more than 340,000 reports globally, marking its largest outage by Downdetector report volume in more than a year.


🚨 BREAKING: The website for the Republican convention in Dallas keeps redirecting to the DOJ's page for the Epstein files.

ATF is aware of claims concerning the possible publication of data allegedly obtained during the previously disclosed cybersecurity incident involving a standalone system used in connection with CALEA. We are working with @TheJusticeDept and other federal partners to assess these claims and take appropriate actions. As stated previously, the affected system was separate from ATF’s enterprise network. ATF has not confirmed the authenticity, nature, or scope of the materials at issue. More at atf.gov/news/press-rel….
User reports indicate problems with Quickbooks Online since 4:25 PM EDT. How is it affecting you? #QuickbooksOnlineDown downdetector.com/status/quickbo…

Anthropic Users Hit by Infostealer Attacks, Session Thefts: bit.ly/3T57u9y by Jai Vijayan

Today, the @FBI and @TheJusticeDept announced the disruption of a global botnet used by Chinese state-sponsored group known as QTFY to target U.S. critical infrastructure. Our investigation attributes QTFY to the Nanjing Xinjiuwei Network Technology Company, which sells stolen data and hacking services to Chinese military and intelligence agencies. Their services include a scanning platform that scours the internet for vulnerable smart devices—like home routers and security cameras—infects thousands of them, and feeds them into a botnet, or a network of machines secretly controlled by the adversary. These platforms hide the origin of PRC-linked cyberattacks. Thanks to the work of @FBISanDiego, FBI Cyber Division, and partners at DOJ—we shut those platforms down 🔗justice.gov/opa/pr/justice…

🚨🇨🇳 FBI knocks China-linked QScan and QTRouter hacking infrastructure offline The DOJ and FBI seized domains powering two hacking platforms operated by QTFY, a Chinese state-sponsored group tied to Nanjing Xinjiuwei Network Technology Company. U.S. officials say QTFY has compromised or targeted sensitive networks including NASA, the Federal Reserve, Department of Energy, DOJ, HHS, NIH, and the U.S. Senate. QScan automatically scans for and infects thousands of IoT devices worldwide. Those compromised devices are then incorporated into QTRouter, an obfuscation network combining hacked IoT devices, commercial proxies, and leased VPS infrastructure to hide the China-based origin of intrusion activity. Court documents say QTFY sells hacking services to paying customers including China's Ministry of State Security and People's Liberation Army. Because the seized domains were hard-coded into QScan and QTRouter for authentication and communications, the FBI says the operation rendered both platforms inoperable. The infrastructure has been linked to malicious activity dating back to at least 2018. Seized: qtproxy[.]xyz Source: justice.gov/opa/pr/justice…

Meta agrees to $17.1 billion settlement over alleged harms to children #Meta #Facebook #Instagram cyberinsider.com/meta-agrees-to…
🚨We are seeing increased targeting of PLCs in the Water and Wastewater Systems Sector. Owners, operators, & integrators should disconnect PLCs & internet-exposed OT assets ASAP to reduce risk of disruptions, configuration changes, & physical damage. 🔗 go.dhs.gov/5sC

Patriot shows Flock cameras track him and his PHONE as he walks by Flock emits Blue Tooth signal for phone connection and tracking
Unpatched Claude for Chrome Flaw Lets Extensions Read Gmail, Calendar securityweek.com/unpatched-clau…

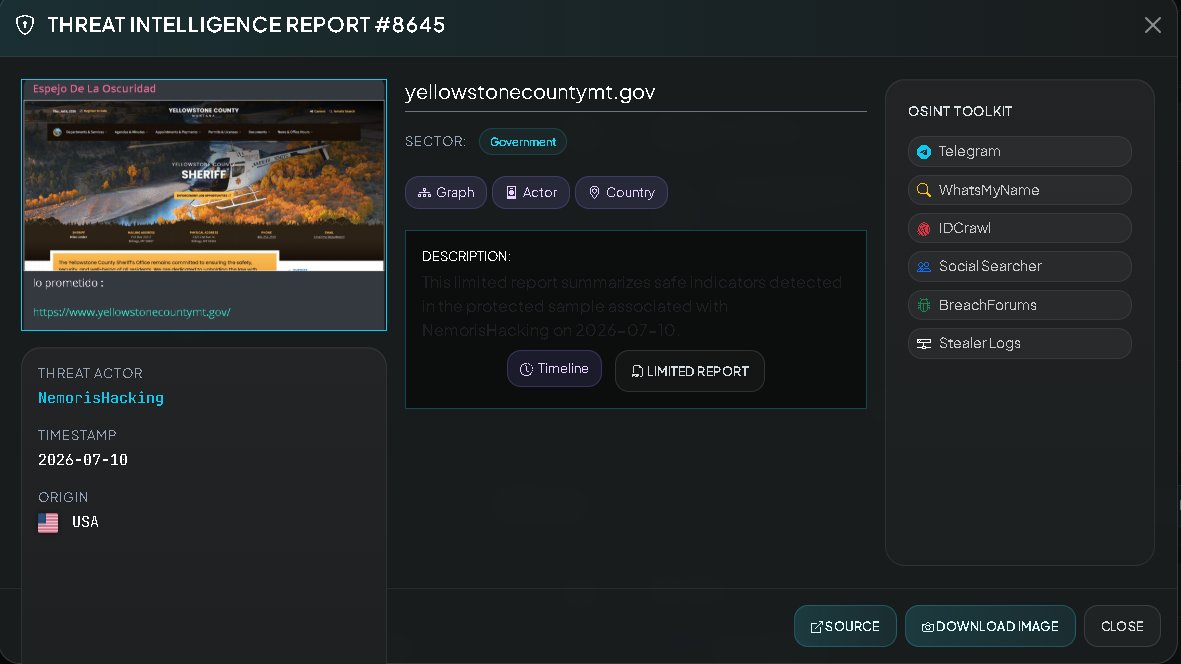
🚨 🏛️ 🇺🇸 CYBER INTELLIGENCE ALERT / ALLEGED DATABASE COMPROMISE — GOVERNMENT AND PUBLIC SAFETY SECTOR (USA) [STATUS: ALLEGED DATA LEAK / UNCONFIRMED / SOURCE: CLANDESTINE CHANNEL (MIRROR OF DARKNESS) / DATE: JULY 10, 2026] THE "NEMORISHACKING" ACTOR CLAIMS DATA EXFILTRATION FROM YELLOWSTONE COUNTY, MONTANA, BY SPREADING FILES LINKED TO THE JUVENILE SERVICES CENTER Through technical monitoring of criminal dissemination channels and data leak forums, a post has been intercepted that allegedly compromises the confidentiality of local computer systems in North America. The threat actor using the alias NemorisHacking, operating within the clandestine channel "Espejo De La Oscuridad" (Mirror of Darkness), has announced the alleged exfiltration of databases belonging to the government infrastructure of Yellowstone County, Montana (yellowstonecountymt.gov). As a proof of concept (PoC), the attacker has published two structured .json files that directly reference the Yellowstone Youth Service Center. 🏢 Allegedly Affected Entity: Yellowstone County Government, Montana, United States (including, indirectly, portals indexed to the local Sheriff's Office). 👤 Threat Actor: NemorisHacking. ⚔️ Volume and Files Compromised According to the Announcement: Two logical extracts named Yellowstone_Youth_Service_Center_-_MT.json and Yellowstone_Youth_Service_Center_-_2MT.json, each with a size of 242.4 KB. 🔍 Verification Status: UNCONFIRMED BY US LOCAL OR FEDERAL AUTHORITIES. As of July 10, 2026, the Yellowstone County Administration, the Sheriff's Office, or CISA have not issued any official statements acknowledging an intrusion into their servers or a loss of control over their databases. This event should be handled under the strict status of SUSPECTED COMPROMISE. 🛡️ PREVENTIVE TECHNICAL RECOMMENDATIONS FOR CONTAINMENT (SOC / PERIMETER DEFENSE) Information security officers for local government portals are urged to implement immediate hardening controls: 🛑 Database and API Endpoint Query Audit: Conduct a forensic investigation of database server and management system logs at the Youth Service Center to detect anomalous spikes in data exports or massive queries that match the size of JSON files published in the last week. 🔑 Repository and Backup Configuration Review: Verify that institutional API endpoints or cloud storage buckets are not publicly exposed without authentication, and immediately revoke outdated passwords and API keys. 📊 MONITORING AND EVALUATION OF GOVERNMENT INFRASTRUCTURE Intelligence System: analyzer.vecert.io Monitoring Console: monitor.vecert.io #CyberSecurity #USA #Montana #YellowstoneCounty #DataLeak #YouthServiceCenter #JSONExposure #GovBreach #SheriffOffice #NemorisHacking #ThreatIntelligence #CyberAlert #VECERT #Infosec #UnverifiedIncident
Xbox CEO Asha Sharma is now an official advisor for the U.S. Federal Reserve. She's leading a task force to address employment and productivity in the U.S. and will directly influence government decisions.


Army orders mass shutdown of official social media accounts militarytimes.com/news/your-army…
🚨Cyber Alert ‼️ 🇺🇸🇨🇦🇲🇽🇧🇷 - 𝗡𝗶𝘀𝘀𝗮𝗻 𝗔𝗺𝗲𝗿𝗶𝗰𝗮𝘀 Nissan Americas disclosed a data breach after hackers exploited the Oracle PeopleSoft zero-day (CVE-2026-35273), potentially exposing current and former employees' personal, financial, tax, and national identification data across the U.S., Canada, Mexico, and Brazil. Threat actor: Not Specified (campaign linked to ShinyHunters) Sector: Manufacturing Data exposure (claimed): Not specified Data type: Employee data Observed: Jun 29, 2026 Status: Confirmed ESIX©: 5.78 Full details and impact assessment on HackRisk.io

US Supreme Court limits police access to people’s location history cyberinsider.com/us-supreme-cou…

Aileen @Aileen345
67 Followers 1K Following I do not wait for opportunities; I create them. Gentle ✨yet firm independent yet radiant this is the person I am becoming.✨
Rouie @Rouie2115cz
111 Followers 4K Following Believe that life is worth living and your belief will help create the fact
haru @his4uht
217 Followers 2K Following
khong tjen huy @tjenhuy
671 Followers 4K Following
SANS.edu Internet Sto... @sans_isc
118K Followers 86 Following @[email protected] - https://t.co/8IgCGtJnZd - Global Network Security Information Sharing Community -
U.S. Cyber Command @US_CYBERCOM
144K Followers 255 Following Official Twitter page of U.S. Cyber Command (Following, retweets and links do not equal endorsement)
DHS Science and Techn... @dhsscitech
33K Followers 385 Following Research and development arm of the Department of Homeland Security. Likes, retweets, etc. ≠ endorsement. Comment Policy: https://t.co/HQr5xUZMhy
Information Security ... @Info_Sec_Buzz
21K Followers 2K Following Delivering the latest in #cybersecurity news, trends, insights, and top #infosec blogs for the cybersecurity community. Stay informed, stay secure!
ISMG Network News @ISMG_News
4K Followers 1K Following ISMG is a global leader in cybersecurity education, intelligence and research with 38 media properties focused on #cybersecurity news.
SECURITY Magazine @securitymag
28K Followers 201 Following Security magazine is designed and written for business-minded executives who manage enterprise risk and security. https://t.co/oa59C5wGbc
Bad Packets by Okta @bad_packets
51K Followers 2 Following We provide cyber #threatintel on emerging threats, DDoS botnets, and network abuse.
SANS Offensive Operat... @SANSOffensive
75K Followers 578 Following More Offensive Than Ever #PenTest | #PurpleTeam | #RedTeam | #ExploitDev Training, Certification, and Research
TypeScript @typescript
423K Followers 49 Following TypeScript is a language for application-scale JavaScript development. It's a typed superset of JavaScript that compiles to plain JavaScript.
Stack Overflow @StackOverflow
256K Followers 232 Following Stack Overflow empowers the world to develop technology through collective knowledge.
Soufiane @S0ufi4n3
14K Followers 240 Following A random infosec/science enthusiast guy... This account is personal and only reflects my opinions, not those of my employer...and if it hurts your feelings🖕
ESET Research @ESETresearch
36K Followers 32 Following Security research and breaking news straight from ESET Research Labs.
Tommy M (TheAnalyst) @ffforward
15K Followers 199 Following Threat Researcher @proofpoint | @Cryptolaemus1
DarkFeed @ido_cohen2
48K Followers 0 Following DarkFeed: Cyber Threat Intelligence Platform, Putting things at order in the ransomware crazy world #OSINT | #Ransomware | #Cyberattacks | #Hacktivism

TechTarget News @TechTargetNews
33K Followers 1K Following Sharing the latest tech news, tips and in-depth insights, covering AI, cloud, cybersecurity, DevOps and more from the Editorial team at @InformaTTGT!
Shadow Chaser Group @ShadowChasing1
11K Followers 573 Following Shadow Chaser Group is a sub-group of the GcowSec team which consists of college students who love it.Shadow Chaser Group focused on APT hunt and analysis
Group-IB Threat Intel... @GroupIB_TI
17K Followers 182 Following Official account of the @GroupIB Threat Intelligence Unit. Latest research, analytics, IOCs and threat alerts.
Bill Gertz @BillGertz
70K Followers 3K Following Washington Times national security correspondent | Covers China | Latest book: Deceiving the Sky https://t.co/mZPoNQB4dl
Virus Bulletin @virusbtn
62K Followers 1K Following Security information portal, testing and certification body. Organisers of the annual Virus Bulletin conference. @[email protected]
Cisco Enterprise Netw... @CiscoNetworking
182K Followers 310 Following Secure by design, purpose-built for the AI Era, simplified with AgenticOps.
It's FOSS @Itsfoss
170K Followers 192 Following Linux and Open Source Web Portal 🐧 Follow us to - Get the latest Linux and Open Source news 📰 - Learn Linux tips and tutorials 💡 - Enjoy Linux memes 🤣
Real Python @realpython
267K Followers 164 Following Online #Python Training & Expert Community: Tutorials, Video Courses, Books, Quizzes...and More! Join 1M+ Pythonistas at https://t.co/VpjtGxdL7J
DevOps.com @devopsdotcom
58K Followers 1K Following Where the world meets DevOps. Powered by @TechstrongGroup.
Cybersecurity @ NIST @NISTcyber
100K Followers 520 Following Official handle covering all things cybersecurity at NIST
Rob T. Lee @robtlee
27K Followers 1K Following Chief AI Officer, Chief of Research, @SANSInstitute | Cybersecurity Expert & Threat Hunter | Godfather of DFIR | Technical Advisor to US Govt
0xor0ne @0xor0ne
94K Followers 508 Following Cybersecurity | Reverse Engineering | Vulnerability Research | Embedded & Silicon Security | My Tweets, My Opinions :)
Luke Stephens (hakluk... @hakluke
101K Followers 2K Following Dad x3, hacker (cybersecurity), marketing expert, serial entrepreneur. CEO of cybersecurity companies: Ironbark Cyber, HackerContent, TRIAGERS™.
Florian Roth ⚡️ @cyb3rops
224K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
Bug Bounty Village @BugBountyDEFCON
10K Followers 609 Following Official X account for the Bug Bounty Village @DEFCON. Founded by @infinitelogins and @arl_rose.
JFrog Security @JFrogSecurity
6K Followers 309 Following The JFrog Security Research Team empowers developers and companies to excel by identifying, prioritizing, and mitigating software risks.
Katie🌻Moussouris (... @k8em0
110K Followers 10K Following @LutaSecurity CEO @payequitynow MIT&Harvard visiting scholar, @MasonNatSec fellow, 1/2 Chamoru, hacker @k8em0.bsky.social Legacy blue check
National Cybersecurit... @StaySafeOnline
187K Followers 1K Following The National Cybersecurity Alliance is a nonprofit that empowers people to use technology safely & securely. Co-leads Cybersecurity Awareness Month
SC Media @SCMagazine
119K Followers 2K Following The official Twitter feed for all things IT security. A CyberRisk Alliance Resource.
HackerOne @Hacker0x01
343K Followers 3K Following HackerOne makes security continuous. We unite AI and human insight through a unified platform to expose risk and eliminate it.
Hackmanac @H4ckmanac
129K Followers 371 Following We track verified, real-world cyber attacks to help you develop effective Cybersecurity strategies. Try https://t.co/eB7qgxKFAa, your Strategic Threat Intelligence platform
Cybernews @Cybernews
72K Followers 401 Following Proving that cybersecurity is everyone's business. We research what others skip, expose what's buried, and know that the real story is never on the surface.
9to5Linux @9to5linux
65K Followers 170 Following Covering latest Linux and Open Source news, apps, security, Raspberry Pi & more! Buy us a ☕: https://t.co/rZJxF0ek6Q
The DFIR Report @TheDFIRReport
70K Followers 0 Following Real Intrusions by Real Attackers, the Truth Behind the Intrusion
SANS Institute @SANSInstitute
195K Followers 412 Following SANS is the most trusted and by far the largest source for information & cyber security training, certification and research in the world.
NSA Cyber @NSACyber
158K Followers 12 Following We protect our nation’s most sensitive systems against cyber threats. Likes, retweets, and follows ≠ endorsement.
publiclyDisclosed @disclosedh1
69K Followers 2 Following This is an unofficial HackerOne public disclosure watcher who keeps you up to date about the recently disclosed bugs. By @NOBBD
Cyber Security News @The_Cyber_News
73K Followers 286 Following World’s #1 Largest Cyber Security News 📰 Platform For Security Professionals. Get Latest #CybersecurityNews #HackingNews, #Cyberattack, #Threats & #breaches
CVE Announcements @CVEannounce
26K Followers 5 Following Account maintained by the CVE™ Program to update the community on CVE-related announcements. https://t.co/2P9qfFrKeu
CyberInsider @CyberInsidercom
14K Followers 85 Following Reliable cybersecurity news and in-depth resources, written by industry experts. DMs open for tips ✉️
Threat Intelligence @threatintel
115K Followers 365 Following Symantec and Carbon Black's threat hunters bring you the latest threat intelligence from the IT security world.
watchTowr @watchtowrcyber
13K Followers 12 Following watchTowr enables organizations to get ahead of in-the-wild exploitation with Preemptive Exposure Management technology.
Decker Eveleth @dex_eve
24K Followers 846 Following Nukes & deterrence analyst at @CNA_org. @reed_college_, @MIIS alum. Former @JamesMartinCNS. Bylines @NKNewsorg @ForeignPolicy @survivaleditors Views my own.
Black Hat @BlackHatEvents
428K Followers 2K Following The World's Premier Technical Cybersecurity Conference Series
Windows Update @WindowsUpdate
91K Followers 508 Following Sharing the latest Windows as a service updates. For immediate assistance, please reach out to @MicrosoftHelps.You might like